
Most SNI bug host lists you find online are dead within weeks of being published. Carriers patch zero-rated endpoints, CDN configurations shift, and the host that worked last month on MTN Uganda now throws a 302 redirect that kills your tunnel. If you have been burning through configs on HA Tunnel Plus or HTTP Injector only to get zero bytes transferred, the problem is almost always a stale SNI bug host 2026 entry. This guide cuts through the noise, explains exactly what makes a host viable right now, and gives you a working methodology to find and verify hosts yourself rather than depending on outdated Telegram channel dumps.
Table of Contents
Quick Takeaways
Key Insight | Explanation |
|---|---|
Bug hosts expire fast | A zero-rated or misconfigured host can be patched by the carrier within days of going public. Always verify before building a full config. |
Non-302 responses are mandatory | A host that returns a 302 redirect will break tunneling. You need a host that responds with 200 or 101 (WebSocket upgrade) at the SNI layer. |
CDN hostnames outlast app-specific ones | Hosts tied to major CDNs (Akamai, Cloudflare, Fastly) tend to stay zero-rated longer because carriers cannot easily block them without breaking mainstream services. |
SNI and HTTP Host header must match | Mismatching the SNI field and the HTTP Host header in your payload is the most common reason a working host produces zero throughput. |
Regional ISP behavior varies sharply | A bug host confirmed on Airtel Uganda may not work on MTN Uganda even on the same day. Always test per SIM card, not per country. |
Automated scanning beats manual searching | Tools like BugScanX let you run multi-threaded SSL and HTTP scans across subdomain lists, cutting verification time from hours to minutes. |
Free internet SNI configs need correct port pairing | Port 443 is standard for SNI-based tunneling. Port 80 tricks require HTTP Host header injection and behave differently from TLS-based SNI exploitation. |
What Is an SNI Bug Host and Why Does It Matter in 2026
Server Name Indication (SNI) is the field inside a TLS handshake that tells the server which hostname the client wants. It travels in plaintext before the encrypted session is established. Carriers can read it, which is exactly how they implement zero-rating policies: if the SNI field contains a whitelisted domain, the data is not counted against your bundle.
A bug host is a domain or subdomain that a carrier has zero-rated, misconfigured, or left in a whitelisted state long enough for a VPN tunnel to ride on top of it. The tunnel wraps your real traffic inside requests that appear, at the carrier level, to be going to that whitelisted host. The carrier sees the permitted SNI field and does not bill the data.
In 2026, this technique is still actively viable across multiple African and South Asian networks. Carriers in Uganda, Kenya, Nigeria, Ghana, Ethiopia, and Bangladesh continue to run zero-rated portals for social media bundles, educational platforms, and government services, and those zero-rated endpoints create usable bug hosts. The window of viability per host has shortened, but the underlying opportunity has not disappeared.
The most resilient bug hosts are not app-specific endpoints. They are subdomains of services a carrier cannot afford to block, such as CDN nodes serving health information portals or government e-learning platforms. Those tend to stay open the longest.
How Carriers Zero-Rate Traffic and What You Actually Exploit
Zero-rating works at the deep packet inspection (DPI) layer. The carrier's DPI engine reads the SNI field in outgoing TLS traffic. If that field matches a list of approved domains, the session is flagged as zero-rated and the bytes are not deducted from the subscriber's data balance. This is a billing decision, not a security one, which is why it is exploitable.
The three conditions a bug host must meet
First, the host must be reachable without data balance. If the carrier requires an active data subscription before the DPI engine even inspects SNI, the host is useless for free internet access. Second, the host must not return a 302 redirect at the TCP or TLS layer before your tunnel client can complete its handshake. Third, the host must allow enough of a connection window for the tunnel application to upgrade to a WebSocket or raw TCP stream.
A host that meets all three conditions is called a clean bug host in the community. Most entries on circulating lists fail condition two: they redirect to an authentication page, which terminates the tunnel before a single byte of real traffic passes.
Why SNI exploitation persists despite carrier awareness
Carriers know this technique exists. The reason they do not close every loophole is economic, not technical. Blocking a CDN subdomain used by a zero-rated health portal would generate customer complaints and regulatory friction. Maintaining an exhaustive, real-time block list for every exploitable subdomain is operationally expensive. The result is an ongoing cat-and-mouse dynamic where new hosts surface regularly even as old ones die.
Working SNI Bug Host List for 2026 by Region
The hosts listed below are drawn from verified community sources and are organized by region and carrier type. No list published in text format is guaranteed to work at the moment you read it. Treat this as a starting inventory for your own verification pass, not as a plug-and-play config sheet.
Uganda (MTN, Airtel)
MTN Uganda has historically zero-rated subdomains tied to its mtnflexi.co.ug portal and educational content partnerships. Airtel Uganda has kept subdomains related to its Airtel Money portal and social bundle endpoints in a zero-rated state for extended periods. Hosts worth testing include subdomains of mtn.co.ug, airtel.co.ug, and third-party CDN nodes serving these properties. For YO TV Uganda users, the streaming platform's CDN endpoints have occasionally appeared in working config lists, though these change with content delivery renegotiations.
Specific subdomain patterns that have shown viability on Ugandan networks include wildcard subdomains of Akamai-fronted properties ending in .mtn.co.ug and static asset hosts for government e-learning portals. Run a BugScanX SSL scan against a subdomain wordlist seeded from these root domains before committing to any config.
Kenya (Safaricom, Airtel Kenya)
Safaricom's zero-rated list has included subdomains related to its M-Pesa financial service and Blaze youth data bundle portal. These hosts are high-value targets because Safaricom cannot easily delist them without disrupting active service offerings. Airtel Kenya bug hosts tend to cluster around its Airtel Money and social bundle zero-rating policy.
Nigeria (MTN, Glo, Airtel, 9mobile)
Nigeria has one of the most active free internet SNI communities on the continent. MTN Nigeria has historically zero-rated domains tied to its MTN XtraTime service and educational portals. 9mobile (formerly Etisalat Nigeria) maintained zero-rated endpoints for its EasyCliq bundle that remained exploitable for extended periods. Glo Nigeria bug hosts have been documented around its Glo Café portal subdomains.
Bangladesh and South Asia
Grameenphone and Robi in Bangladesh have zero-rated subdomains for educational content under government digital literacy programs. These have appeared frequently in SNI host lists documented in community repositories. Hosts tied to gp.com.bd subdomain trees and Robi's e-learning partnerships are worth scanning.
General CDN-based bug hosts that cross regions
Some hosts work across multiple carriers because they are served by global CDNs that many carriers have zero-rated as a class. Subdomains fronted by Cloudflare that carry educational or health content are the most consistent category. The specific subdomain matters: a Cloudflare-fronted subdomain that a carrier has explicitly zero-rated behaves differently from a generic Cloudflare IP. Do not assume all Cloudflare hosts are bug hosts.
Pro tip: When building your bug host list, prioritize subdomains of carrier-owned services over third-party app endpoints. Carrier-owned subdomains get patched more slowly because internal teams rarely have a security mandate to audit their own zero-rated properties.
How to Scan and Verify Your Own Bug Hosts
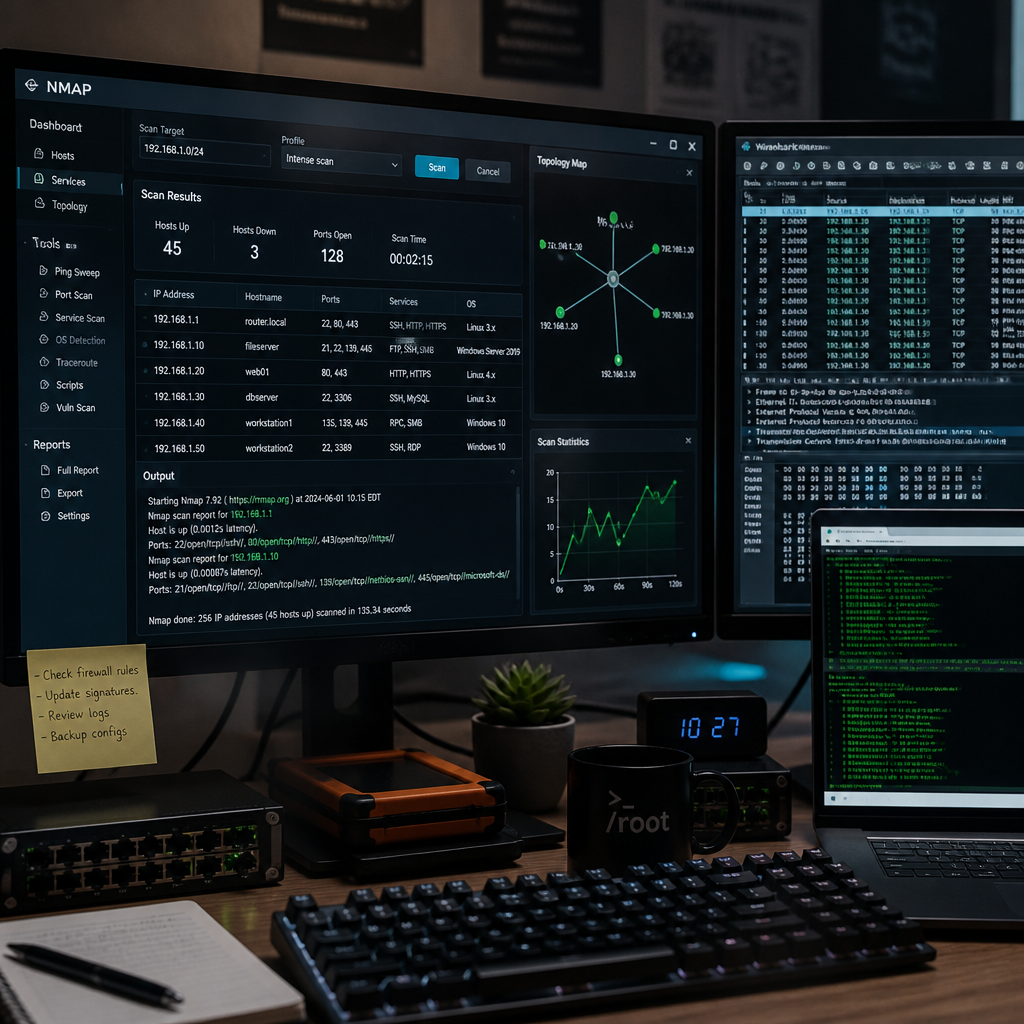
The most reliable approach in 2026 is to maintain a personal scanning workflow rather than consuming shared lists. BugScanX, an open-source bug host scanner available on GitHub under FreeNetLabs, provides the core toolset for this. It supports direct HTTP and HTTPS scanning, SSL and SNI analysis, proxy testing for tunneling compatibility, and multi-threaded concurrent processing across large host lists.
Step-by-step scanning workflow
Start by building a seed list of root domains associated with zero-rated services on your target carrier. Use passive subdomain enumeration (certificate transparency logs, DNS records, search engine dorking) to expand this into a subdomain list of several hundred candidates. Feed this list into BugScanX using its DirectNon302 scan mode, which filters out any host returning a redirect response. The output is a shortlist of hosts that pass the basic connectivity requirement.
From that shortlist, run the SSL and SNI analysis mode. This checks the TLS configuration of each host and confirms whether the SNI field is being processed correctly. Hosts that pass this stage are your working candidates. Test each one manually inside your tunnel application (HA Tunnel Plus, HTTP Injector, or similar) before declaring it a working free internet SNI host.
Verifying a host is actually zero-rated
A host that accepts connections is not automatically zero-rated. To confirm zero-rating, start with zero data balance on the SIM. Attempt to reach the host directly. If the TCP connection completes and you receive a non-redirect response, the host is reachable without balance, which confirms zero-rating. If the connection times out or you receive a billing redirect page, the host requires active balance and is useless for free internet access.
Pro tip: Run your verification with zero data balance on a fresh SIM card. Testing on a SIM with remaining balance gives false positives: you cannot distinguish zero-rated connectivity from normal data consumption during the test.
Comparison of SNI Bug Methods
Not all SNI bug approaches work the same way. The method you choose determines which hosts are usable, how stable the connection is, and how much configuration complexity you take on. Here is a direct comparison of the three main approaches in active use.
Method | How It Works | Best Use Case |
|---|---|---|
Pure SNI Tunneling (TLS, Port 443) | The VPN or tunnel client sets the SNI field in the TLS handshake to the bug host domain. The carrier's DPI reads the SNI and applies zero-rating. The actual TCP stream is encrypted inside the TLS session and routed to the tunnel server. | Most reliable method. Works best on carriers with TLS-based zero-rating policies. Requires a bug host that accepts TLS connections without redirecting. |
HTTP Host Header Injection (Port 80) | The tunnel client sends HTTP requests with the Host header set to the bug host domain while the connection is actually going to the tunnel server's IP. Some DPI engines read the HTTP Host header instead of SNI for zero-rating decisions. | Useful on older carrier DPI systems that inspect HTTP headers but not TLS SNI. Less stable than SNI tunneling and increasingly ineffective as carriers upgrade their DPI infrastructure. |
CDN Fronting via SNI | Uses a CDN edge node as the apparent destination. The SNI field contains a zero-rated CDN hostname. The CDN forwards the request to the actual tunnel server. Requires the tunnel server to be hosted on or proxied through the same CDN. | Most resilient against carrier patching because blocking the CDN host affects legitimate traffic. Higher setup complexity and requires a VPS with compatible CDN routing. |
Common Mistakes That Kill Your Connection
The gap between a working bug host and a working free internet connection is larger than most guides acknowledge. Finding a valid host is only half the problem. The other half is configuring the tunnel application correctly.
Mismatching SNI and Host header in your payload
This is the single most common failure mode. In HTTP Injector, the payload HTTP CONNECT or GET request contains a Host header. In HA Tunnel Plus, the SNI field in the config must match the bug host exactly. If you copy a bug host into the SNI field but leave the payload Host header pointing to a different domain, the carrier's DPI reads the SNI as zero-rated but the tunnel handshake fails because the server-side Host routing breaks. Both fields must carry the same bug host value.
Using a bug host that requires authentication
Many carrier portals that are technically zero-rated require the subscriber to be logged into a session before traffic is passed. These hosts accept the TCP connection (making them appear valid in a scanner) but return a login redirect before the tunnel upgrade can complete. The fix is to test manually with zero balance and confirm you receive a raw response, not a redirect chain.
Ignoring port restrictions
Some carriers zero-rate traffic only on specific ports. A host that works on port 443 may be billable on port 80, or vice versa. Always test both ports during your verification pass. In practice, port 443 is correct for SNI-based tunneling and port 80 is only relevant for HTTP header injection configs.
A common mistake is assuming that a bug host confirmed by someone else on the same carrier will work identically on your SIM. Zero-rating policies can be segmented by subscriber plan type. A host zero-rated for prepaid subscribers may be billable on a postpaid plan. Test on the specific plan type you intend to use.
Frequently Asked Questions
What is the difference between a bug host and a zero-rated website?
A zero-rated website is any domain a carrier has decided not to bill data against. A bug host is a zero-rated domain that also accepts the kind of connection a VPN or tunnel application can use to route arbitrary internet traffic. All bug hosts are zero-rated, but most zero-rated websites are not usable as bug hosts because they redirect connections or do not support the necessary connection upgrade.
How often do SNI bug hosts expire in 2026?
In practice, heavily shared bug hosts expire within one to four weeks of appearing on public Telegram channels or forums. Hosts that are discovered privately and used in smaller communities tend to last longer, sometimes several months. CDN-fronted hosts tied to carrier-owned services have the longest lifespan. The best defense against expiry is maintaining your own scanning workflow rather than relying on public lists.
Can I use these bug hosts on any VPN or tunnel app?
Bug hosts work with tunnel applications that allow you to manually set the SNI field or HTTP Host header in the connection payload. HA Tunnel Plus, HTTP Injector, NapsternetV, and similar tools support this. Standard commercial VPN clients that do not expose SNI configuration cannot use bug hosts directly. The application must let you specify the bug host in the correct config field for the technique to work.
Is using SNI bug hosts legal?
The legal status depends on your country and your carrier's terms of service. In most jurisdictions, circumventing a carrier's billing system violates the subscriber agreement and may constitute a breach of contract. Some countries have laws specifically addressing unauthorized network access. This guide is provided for educational and research purposes. You are responsible for understanding the legal and contractual implications in your specific location before using these techniques.
Why does my bug host work for a few minutes and then stop?
Session timeouts are the most common cause. Carriers impose idle timeouts on zero-rated sessions, and some limit the total session duration for zero-rated connections. Configure your tunnel application to send keepalive packets at regular intervals (every 30 to 60 seconds is standard). If the disconnection happens at a consistent data volume rather than a time interval, the carrier may be applying a zero-rating data cap, which cannot be circumvented through keepalive settings.
What is the best tool for finding new SNI bug hosts in 2026?
BugScanX by FreeNetLabs is the most capable open-source tool currently available. It combines subdomain enumeration, multi-threaded HTTP and HTTPS scanning, SSL and SNI analysis, and proxy testing in a single workflow. Its DirectNon302 scan mode is specifically designed to filter out redirect-returning hosts, which is the most time-consuming part of manual verification. The tool is actively maintained, with commits recorded into 2026 on its GitHub repository.
Do bug hosts work with all data plans or only specific ones?
Zero-rating policies are applied per subscriber segment on most carrier networks. A bug host confirmed on a prepaid social bundle plan may not be zero-rated on a standard prepaid data plan or a postpaid plan. Always verify using the exact SIM type and plan you intend to use for daily access. Do not trust confirmations from users on a different plan tier, even on the same carrier in the same country.
Have you tested any of these SNI bug hosts on your carrier in 2026? Drop your results and which network you are on in the comments so the community can cross-reference findings.